Security
Your security settings live at /user/security — open the avatar menu and choose Security. The page has tabs for Active Sessions, Two-Factor Auth, Trusted Devices, Login History, Security Alerts and Connected Accounts.
Two-factor authentication and every session feature are available on all plans, including Free. They are not gated.
Two-factor authentication
Section titled “Two-factor authentication”Two methods are supported:
- Authenticator app (TOTP) — any standard app, scanned from a QR code.
- Email verification — a one-time code sent to your account email.
Turn on two-factor
Section titled “Turn on two-factor”Everyone turns this on for their own account, on every plan.
-
Click your avatar at the top right, then Security. On a phone, tap the menu button at the top right first.
-
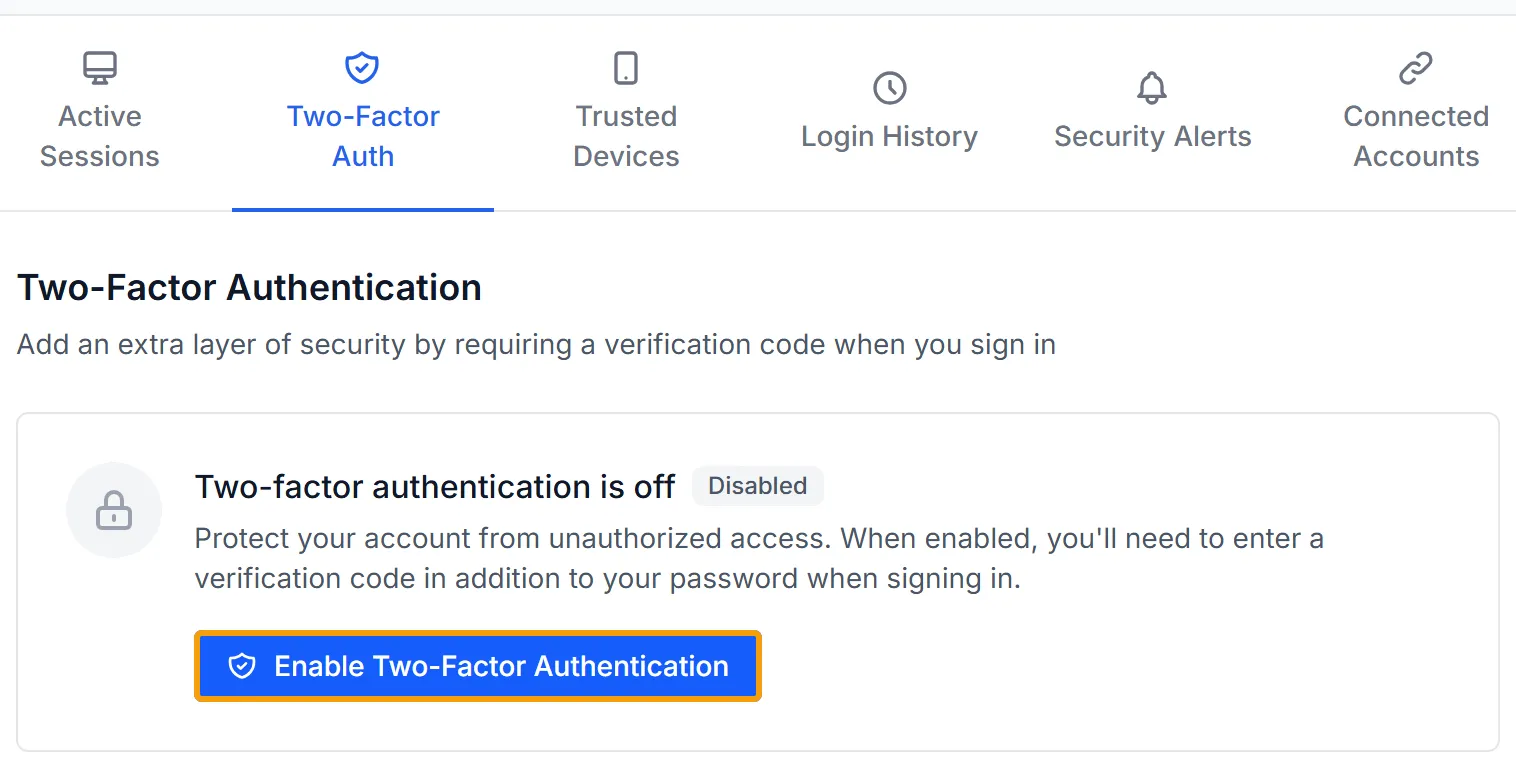
Click the Two-Factor Auth tab (Auth on a phone).
-
Click Enable Two-Factor Authentication.
-
Enter your password, then click Continue.
-
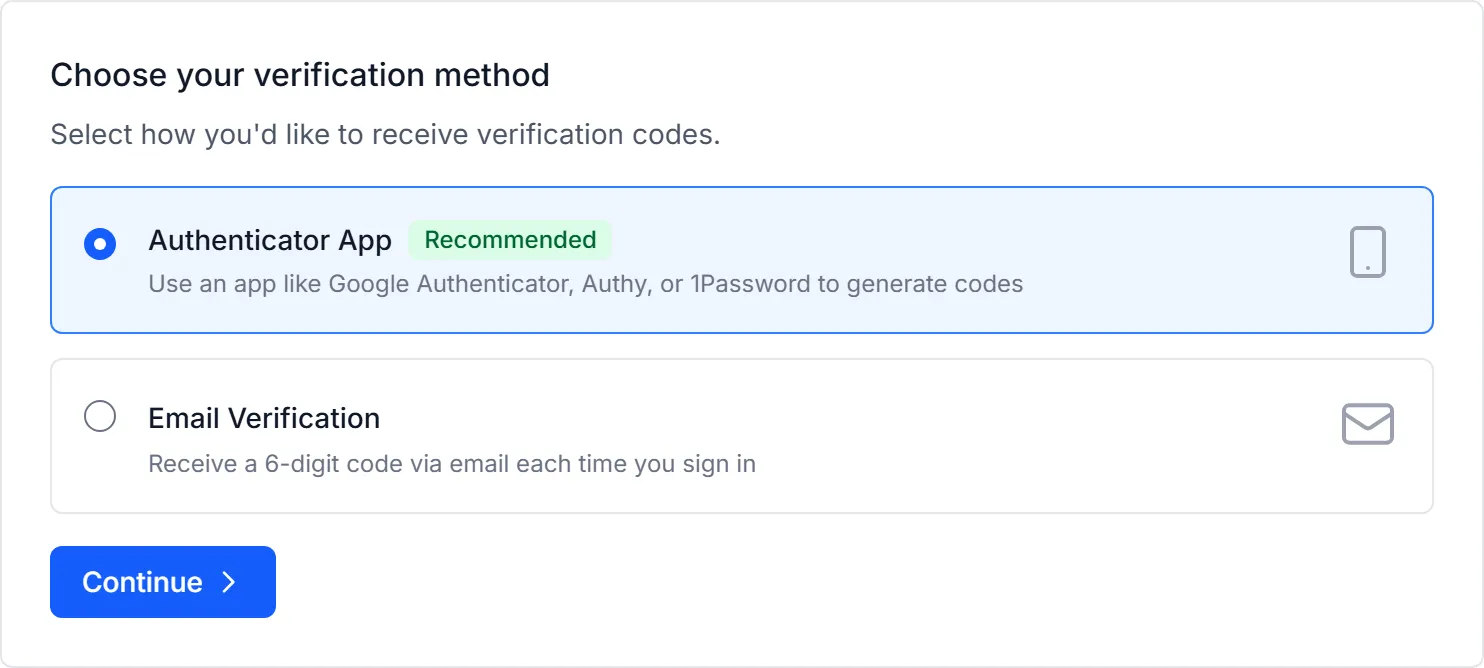
Choose Authenticator App or Email Verification, then click Continue.
-
Enter the 6-digit code:
- Authenticator App: scan the QR code with your app, or enter the key shown beside it. Then type the code the app gives you.
- Email Verification: type the code we emailed you. If it doesn’t arrive, click Didn’t receive the code? Resend.
-
Click Verify & Continue.
-
Under Save your backup codes, click Download or Copy All, and keep the codes somewhere safe.
-
Tick I have saved my backup codes in a secure location.
-
Click Done.
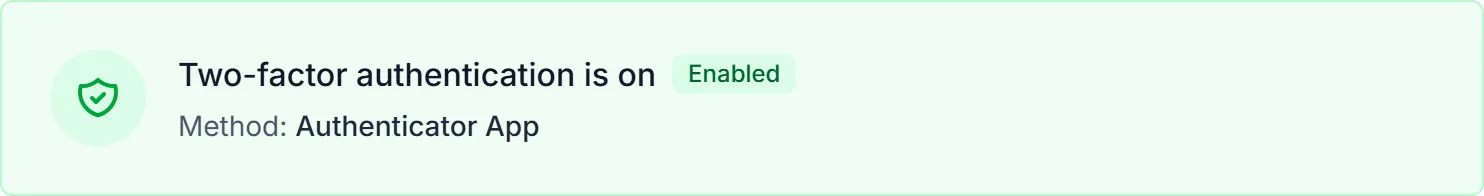
The tab now says two-factor is on, and you’ll be asked for a code when you sign in.
When you enable it you also get 10 backup codes. Each is single-use, and you can regenerate the set at any time from Regenerate Codes — regenerating invalidates the old ones.
A device you mark as trusted stays trusted for 30 days, after which it challenges you again.
Two-factor is enforced at login once you enable it on your own account. There is currently no way for an account owner to require two-factor across their whole team — each person enables it for themselves.
If the email code doesn’t arrive when you sign in
Section titled “If the email code doesn’t arrive when you sign in”We send the code as soon as the sign-in code screen opens.
- Look for an email with the subject Your SurveyRock verification code, including in your spam or junk folder.
- Nothing after a minute? Click Resend code on the same screen. Each code works for 10 minutes, and an earlier code you haven’t used still works until its 10 minutes are up.
- You can request up to 10 codes an hour. After that the screen shows Too many OTP requests; wait and try again later.
- Can’t get into that inbox? Type one of your backup codes into the same box instead.
Active sessions and trusted devices
Section titled “Active sessions and trusted devices”The Active Sessions tab lists where your account is signed in and lets you:
- Revoke an individual session
- Sign Out All Other Devices — ends every session except the one you are using
- Sign Out Everywhere — ends all of them, including the current one
Changing your password also signs out all your other devices.
Sessions last 30 days, or 90 if you chose “remember me” when signing in. There is no configurable idle timeout — a session ends when it expires or when you revoke it.
A display issue to be aware of: the “Current Session” and “Trusted” badges currently appear on every row rather than only the relevant one. The underlying data is correct and revoking works properly; only the badge placement is wrong.
Passwords
Section titled “Passwords”Passwords must be at least 12 characters and no more than 72 bytes (about 72 characters in English; fewer if you use accented letters or emoji, which take more than one byte each). There is no requirement to mix character types — no capital letter, number or symbol is required, because length does more for you than symbol rules do.
Three more checks run on every new password:
- It cannot appear in a list of commonly-used passwords.
- It is checked against Have I Been Pwned, so a password exposed in a known public breach is refused. This uses k-anonymity: only a partial hash prefix leaves our servers, never your password.
- It cannot contain your email address or username.
Change your password from /user/profile, not the Security page.
Protection against password guessing
Section titled “Protection against password guessing”Repeated failed sign-ins are rate-limited per IP address and per account, within a rolling fifteen-minute window, with the delay increasing as attempts continue. Past a threshold, a verification challenge is added.
This is automatic and needs no configuration.
Single sign-on
Section titled “Single sign-on”SAML 2.0 and OpenID Connect are available on Pro and above, configured per workspace under Workspace Settings → SSO. You supply your identity provider’s metadata; we do not need credentials of our own for it.
SSO works only for email domains your workspace has verified. Your identity provider can sign people in with addresses on those domains and no others.
To make SSO the only way in, turn on Enforce SSO in the configuration. Anyone whose email is on one of its verified domains then has to sign in through your identity provider. A password sign-in is refused and sent to your identity provider instead. The account owner keeps a password sign-in, so a broken SSO setup cannot lock everyone out, and can also request an emergency access code at app.surveyrock.com/site/emergency-access. Test SSO with one person before you turn enforcement on.
If you are setting up SSO for the first time, contact us — we would rather walk through the first configuration with you than have you discover a mismatch at the login screen.
Roles and access
Section titled “Roles and access”Five built-in roles:
| Role | Surveys | Sending | Results | Can see PII | Delete surveys | Account admin |
|---|---|---|---|---|---|---|
| Owner | Full | Full | Full | Yes | Yes | Members, settings, branding, billing |
| Admin | Full | Full | Full | Yes | Yes | Members, settings, branding — not billing |
| Editor | Full | Full | Full | No | No | None |
| Viewer | View only | No | View only | No | No | None |
| No access | None | None | None | No | No | None |
The practical differences worth knowing: Admin cannot touch billing — that is Owner only. And Editor cannot see personally identifiable information in responses or delete surveys, which is usually the right default for someone building surveys rather than administering the account.
Custom role presets, permission groups and directory sync are Enterprise features. See Directory sync (SCIM).
Encryption
Section titled “Encryption”- In transit — TLS across the application, the API and the marketing site.
- At rest — the database, file storage and cache are all encrypted at rest.
Your data
Section titled “Your data”Data export, correction, consent preferences and account deletion are at /gdpr/data-privacy-view. That page is not currently linked from the main navigation, so go to it directly.
Retention rules can be set per survey or as an account default, and a nightly job removes data past its retention window. Masking of personally identifiable information in responses is available on Team and above.
If you turn on anonymous responses for a survey, that survey does not record the respondent’s IP address, device or country against their answers. If the survey also reports by team, each response records which team it came from, and every view of a team is held to minimum group sizes. See Collect responses anonymously for what an anonymous response keeps and which views are held back, and Team reports.
A workspace owner or admin can turn off every AI feature for a workspace, so nothing from it is sent to an AI provider. See Turn off AI for a workspace.
Certifications — where we actually stand
Section titled “Certifications — where we actually stand”We would rather be plain about this than let a page imply otherwise.
- GDPR — we align with it. A DPA is available.
- SOC 2 Type II — not held. On our roadmap.
- ISO 27001 — not held. On our roadmap.
- HIPAA — not available. Until it is, we will not accept protected health information or sign a BAA.
If your procurement process requires a certified vendor today, we are not that vendor yet. Tell us your timeline and we will tell you honestly whether it matches ours.